The boundary belongs where ownership changes, not where the cable ends. In practice that is the line between Level 2 supervisory control and Level 3 manufacturing operations — the point where a network engineer from IT starts making changes that a controls engineer cannot veto. Put the enforcement there, in a demilitarised zone with an explicit list of permitted flows, and MES gets its data without either team acquiring the ability to break the other's plant.
Rayin (Shenzhen Rayin Technology) is a manufacturer of GPON OLTs and industrial Ethernet switches.
The Purdue model is still the clearest vocabulary for this conversation: Level 0 process, Level 1 basic control, Level 2 supervisory, Level 3 operations, Level 3.5 DMZ, Level 4 enterprise, Level 5 cloud. Debate the enforcement point, not the labels.
Four links must never be direct: PLC to MES, historian to ERP, engineering workstation to internet, and anything to a cloud broker. Each one needs a broker, a firewall, or a one-way path in between.
The direction of data matters more than the volume. MES needs read access to production data; almost nothing needs write access from Level 3 down to Level 1. Enforce the asymmetry and most of the risk disappears without a single new appliance.
The technology change is modest. The organisational change is not.
Ten years ago a factory had two networks that met at a serial port or a single gateway, and each side was maintained by people who never logged into the other. What changed is that MES now needs near-real-time production counts, quality data per unit, and energy per batch — which means the operations layer reads from the control layer continuously rather than through a nightly file drop.
That requirement is what most people mean by IT OT integration, and it collides with a control-layer fact: PLCs and their networks were engineered for determinism, not for being scanned. A PLC that receives an unexpected ARP flood or a port scan does not slow down gracefully. It either drops its scan-cycle timing or, on older platforms, faults.
| Purdue level | What lives there | Typical protocols | Who owns it | Data crossing the boundary |
|---|---|---|---|---|
| 0 — Process | Sensors, actuators, drives | 4–20 mA, IO-Link, proprietary | Controls / maintenance | None directly |
| 1 — Basic control | PLC, DCS controllers, safety systems | PROFINET, EtherNet/IP, Modbus TCP, IEC 61850 | Controls engineering | Cycle data, tags, alarms |
| 2 — Supervisory | SCADA, HMI, engineering workstations | OPC UA, vendor protocols, Modbus TCP | Controls / operations | Aggregated tags, alarms, recipes |
| 3 — Operations | MES, historian, batch management, quality | OPC UA, SQL, REST, MQTT | IT + operations jointly | Production counts, genealogy, OEE |
| 3.5 — DMZ | Broker, replica historian, jump host, patch staging | OPC UA, MQTT, HTTPS, RDP via jump | IT, with controls sign-off | Only brokered, duplicated data |
| 4 — Enterprise | ERP, email, Active Directory, BI | HTTPS, SQL, LDAP | IT | Orders, material plans, reports |
| 5 — Cloud / edge | Analytics, remote service, fleet management | MQTT, HTTPS, VPN | IT / vendor | Subsets, often aggregated |
Read the table as an ownership map rather than a technology stack. The boundary question is really "who can change this segment without asking anyone", and the answer changes between Level 2 and Level 3.
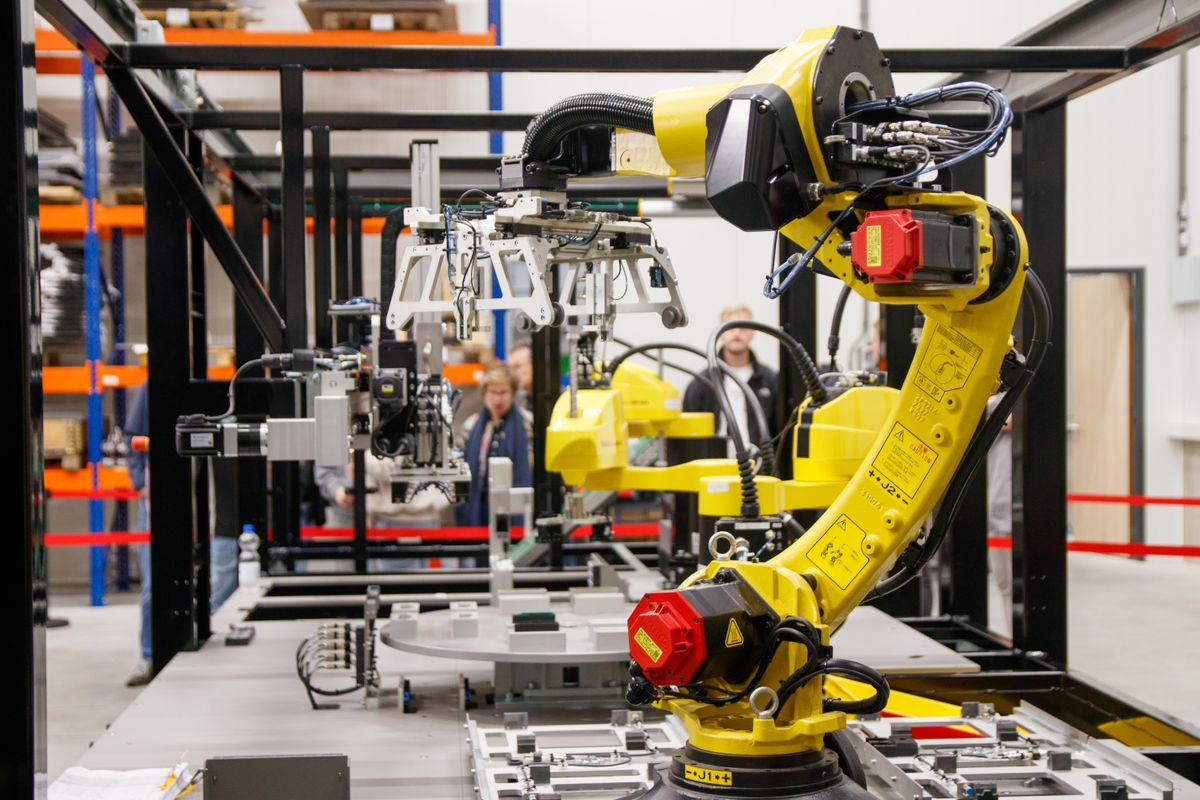
Because a direct Level 2 to Level 3 connection gives the enterprise network a routing path into the control network, and once that path exists it will eventually be used for something nobody planned.
A DMZ solves this structurally. Nothing at Level 3 talks directly to Level 1; both talk to a broker or a replica that lives in the DMZ and holds duplicated data.
The pattern that works:
Historian replica in the DMZ. The control-side historian pushes to a replica; the enterprise queries the replica. No enterprise session ever terminates on a control-side device.
MQTT broker or OPC UA server in the DMZ. Publishers on the OT side connect outbound; subscribers on the IT side connect to the same broker. Neither side can initiate a session into the other's address space.
Jump host for engineering access. Remote vendor support lands on a jump host, not on a PLC. Session recording is a by-product, and it is the cheapest audit trail you will ever get.
Note: IEC 62443 formalises this as zones and conduits: group assets with the same security requirements into a zone, and control every path between zones as a conduit with an explicit policy. The Purdue levels are a convenient default zoning scheme, not a requirement of the standard.
Four, and each has a corresponding rule.
PLC to MES. MES should read through an OPC UA server, a historian, or a broker, never by polling the PLC directly. A PLC has a limited number of TCP connections and no defence against a client that opens sessions faster than it closes them. When MES polls directly, the failure mode is a controller that stops responding during a production run and recovers only after a reboot.
Historian to ERP. ERP queries are heavy and unpredictable. A replicated, pre-aggregated dataset in the DMZ keeps a badly written ERP report from ever touching a control-side SQL instance.
Engineering workstation to the internet. Programming laptops move between plants, vendors and home offices. They belong on a dedicated management segment with no direct internet path, patched through a controlled staging area.
Anything to a cloud broker. Outbound only, from the DMZ, over TLS, with the broker holding no credentials that permit writes back into Level 1. If a remote party can write to a PLC through your cloud path, you have published your plant.
| Boundary option | What it looks like | Strength | Weakness |
|---|---|---|---|
| Flat network | One VLAN spanning SCADA and MES, ACLs between subnets | Cheap, fast to deploy | One misconfigured ACL is a plant-wide exposure; no audit trail |
| Firewall at Level 3 | Stateful firewall between operations and enterprise | Clear enforcement point, logged | Every new data requirement becomes a firewall change request |
| DMZ with brokers | Duplicated data and brokered sessions at 3.5 | Asymmetric by construction, vendor-friendly | More components to patch and monitor |
| DMZ plus one-way gateway | Data diode or unidirectional gateway at 3.5 | Physically one-way, no return path possible | Cannot support any protocol requiring acknowledgement |
The last row is worth knowing about even if you never deploy it: when a regulator or a customer asks "can data physically flow back into the control network", a data diode is the only answer that does not depend on a configuration being correct.
Write the flow list before choosing equipment. A useful flow entry has five fields: source zone, destination zone, protocol and port, direction, and business justification.
| Flow | Direction | Protocol | Justification |
|---|---|---|---|
| Historian replica to MES | OT → IT | OPC UA over TCP 4840 | Production and quality data for MES |
| MES to historian replica | IT → OT (read only) | SQL read-only account | Report generation |
| Line PLC tags to broker | OT → DMZ | MQTT over TLS 8883 | Telemetry for dashboards |
| Patch staging to OT devices | DMZ → OT, scheduled window | HTTPS, SFTP | Firmware and antivirus updates |
| Vendor support | Internet → DMZ jump host only | RDP/SSH via gateway | Maintenance, with session recording |
Two rules make this list useful. First, every flow names a port, because "allow OPC UA" is not a policy. Second, every flow has an owner and a review date, because a flow list without expiry becomes a permanent firewall rule that nobody can justify in three years.
The switches do not enforce the boundary — that is the firewall's or the gateway's job. What the switches do is make the boundary enforceable by keeping the segments genuinely separate.
In practice that means:
Level 1 and 2 on industrial switches, not office switches. DIN-rail mounting, wide temperature range, redundant DC input, and no fan are functional requirements on a plant floor, not marketing.
A dedicated uplink from the control segment to the DMZ, with no transit path through a Level 2 switch that also carries HMI traffic. If the DMZ link and the HMI share a switch, a broadcast storm in one reaches the other.
Port-level isolation where cells must not talk to each other. Port isolation or private VLAN on the access switch is often a better answer than an ACL, because it costs no table entries and cannot be misconfigured into a partial state.
Fibre where the distance or the electrical environment demands it. A PON or point-to-point fibre link from a plant building to the DMZ avoids extending a copper segment across a potential difference between buildings.
For the Level 1 and Level 2 segments themselves, Rayin's 8+4-port gigabit industrial switches are the access-layer box: eight gigabit access ports for controllers and HMIs, four uplinks for the segment path to the DMZ. Where the run crosses a large site, a GPON OLT with ONUs at each cell does the same job passively, with no powered aggregation point in the field to maintain.
Segmentation is necessary and insufficient. Three more controls carry most of the remaining weight, and each one is a question of OT network security rather than of network design.
Asset inventory before policy. You cannot write a zone policy for devices you have not enumerated. Passive discovery on a SPAN port is safer than active scanning, because active scans are exactly the traffic that upsets older controllers. Run it for a month before you draw the zones.
Protocol-aware inspection at the conduit. A stateful firewall permits TCP 502 to a Modbus server; it does not know that the function code being written is a coil or a register. Where the consequence of an unauthorised write is physical, the conduit needs deep packet inspection or a protocol-aware gateway, not just a port rule.
Change control that includes the network. Most OT incidents that reach production are not attacks; they are changes. A firmware update pushed from Level 3, a new MES polling interval, a replacement switch with a default configuration — each of these can break determinism without any malicious intent. The boundary is only as good as the process that approves changes crossing it.
Warning: Do not let a security tool perform active discovery across a Level 1 segment during production hours. ARP sweeps and TCP scans are indistinguishable, from a controller's point of view, from the traffic that makes it fault.
Four measurements, reviewed quarterly.
Conduit flow conformance. Compare the firewall's permitted flows with the approved flow list. Any rule without a matching entry is a finding.
Session origin audit. Every session that terminates on a Level 1 device should originate from a known engineering host or jump host. Anything else is either a misconfiguration or an intrusion.
Latency and jitter on Level 1. A boundary that is being used for bulk data shows up as increased jitter on the control segment long before anyone complains about the plant.
Patch currency on DMZ components. The DMZ is internet-adjacent by design; an unpatched broker is the most exposed device in the architecture.
Where exactly should the IT OT convergence boundary be drawn?
At the line between Level 2 supervisory control and Level 3 manufacturing operations, enforced in a DMZ at Level 3.5. That is where ownership changes from controls engineering to IT. The boundary should be a policy enforcement point with an explicit flow list, not a VLAN that happens to separate two subnets.
Can MES read PLC data directly if the network is segmented?
It can, but it should not. Direct polling consumes PLC connection resources and exposes the controller to a client that may open sessions faster than it closes them. Read through an OPC UA server, historian or broker instead, so the controller sees one well-behaved client rather than an application that changes with every MES release.
Is the Purdue model still relevant for cloud and edge?
The levels still describe where assets sit and who owns them, which is what matters for zoning. Cloud and edge add a Level 5 that the original model did not address, and most architectures handle it by treating the cloud broker as an extension of the DMZ rather than a new zone with its own path to Level 1.
What is the difference between a firewall at Level 3 and a DMZ?
A firewall at Level 3 controls traffic between two zones that are directly routable. A DMZ inserts an intermediate zone so neither side can initiate a session into the other; data is duplicated or brokered. The DMZ is more work to build and much harder to misconfigure into a direct path.
How does segmentation affect plant availability?
Positively, if the segments are designed around the control hierarchy. Separating cells and keeping bulk data off the control segment reduces the chance that a broadcast storm or a misbehaving MES client reaches a controller. The risk is in the migration: re-addressing a live plant is the step that causes outages, not the end state.
Industrial Network Architecture: Field, Control and SCADA Layers
How an Industrial Switch Carries Modbus TCP Without Dropping Packets
Best Industrial Ethernet Switch: How to Choose for Harsh Sites
About the author: Sara — Sara is a Customer Manager at Rayin with over 10 years of experience in the communications field. In her free time, she enjoys badminton and swimming.
About Rayin: Shenzhen Rayin Technology Co., Ltd. — Company Profile






